Patch-Against-Patch: Microsoft’s Record 974-Fix Release Signals a Shift From Discovery to Deployment
Microsoft’s September 2026 Patch Tuesday included at least 974 fixes, its largest single update batch, with two actively exploited zero-days and 113 critical-severity flaws. Year-to-date fixes surpassed 2,600, roughly double Microsoft’s 2020 annual record with three months remaining; Microsoft and other vendors credit AI-assisted discovery for rising patch volume. Experts quoted in the report frame deployment testing and risk-based prioritization, not raw vulnerability count, as the operational constraint.
Microsoft’s September 2026 monthly patch release—listing at least 974 fixes—is a structural event rather than a routine cadence change. It eclipsed the company’s previous monthly record of roughly 570 fixes by about 70%, and it contained two actively exploited privilege-escalation zero-days. The notable shift is not that Windows has more disclosed vulnerabilities; it is that release volume is now growing at a pace that assumes automation inside the vendor while enterprise deployment processes still assume human validation.1
Context
The documented scale anchors are: 974 or more fixes in September; a prior July record of at least 570; a 2026 year-to-date count above 2,600 versus a 1,245 full-year total in 2020; 113 critical ratings; and two zero-days (CVE-2026-81963, CVE-2026-85880) reported as actively exploited. These are release-side metrics, not a live count of exploitable systems.1
Assessment
The report’s own sources suggest the highest-impact inference is the volume-reachability gap: one quoted researcher estimates the subset of flaws that will affect most organizations remains low, while another emphasizes that third-party applications must be regressed before deployment. Read together, they imply that the real exposure is the queueing delay between a published fix and a tested deployment, a delay the record batch may lengthen rather than the number of flaws by itself.1
Caveats
AI hypothesisWhat would change this assessment: evidence that AI-assisted discovery is finding proportionally more reachable, exploitable flaws (more needles, not only hay), or that vendors’ count inflation comes with lower median severity; either would reduce the prioritization-tax interpretation. Conversely, if future month counts plateau while exploitation of known zero-days remains the main threat, the supposed constraint shift toward deployment would be weaker than the record month makes it appear.1
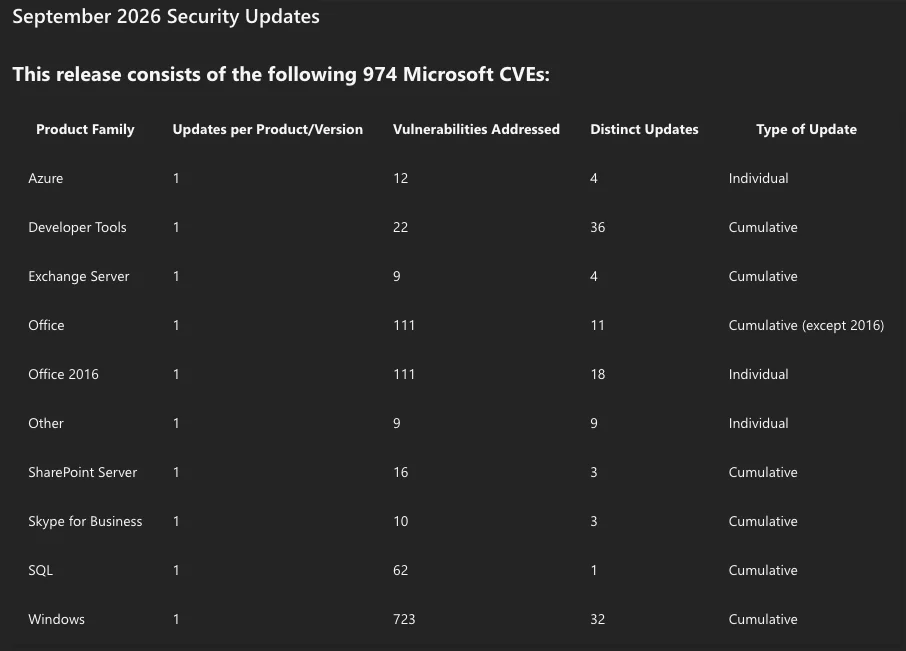
Microsoft Corp. today issued updates to plug at least 974 security holes in its Windows operating systems and other software, by far its biggest single patch batch ever. Microsoft says artificial intelligence is helping to speed the discovery of vulnerabilities, but security experts warn that many organizations already are struggling to prioritize the more human-intensive endeavor of testing and deploying so many fixes each month.
Image: Shutterstock.com, Kirill Makarov.
This month’s patch bundle obliterates the software giant’s previous record set in July, when it released updates for at least 570 security vulnerabilities. September’s Patch Tuesday brings this year’s total to more than 2,600, more than twice Microsoft’s previous record-setting patch year in 2020 (1,245) and with three more months to go.
There are two “zero-day” flaws fixed this month that are being actively exploited: both CVE-2026-81963 and CVE-2026-85880 allow an attacker to elevate their privileges on Windows system.
Fully 113 of the bugs addressed today earned Microsoft’s “critical” rating, meaning they could be abused by malware or miscreants to seize control over a vulnerable Windows machine with little or no help from the user.
Among the more serious critical flaws this month is CVE-2026-69730, a DNS weakness present in Windows Server 2012 onward and on Windows 10. Microsoft warns that an unauthenticated attacker could leverage this weakness simply by sending a specially crafted packet to an affected system, and that it is likely to be exploited.
Also scary is CVE-2026-69829, a critical, remote code execution flaw in the Windows Shell. This vulnerability has a CVSS base score of 9.8 (10 is the most severe), and can be exploited with low attack complexity, no privileges, and no user interaction.
Microsoft’s summary of the security updates released today. Image: msrc.microsoft.com.
Microsoft is hardly alone in shipping monster patch bundles lately. Many other large software companies, including Adobe, Cisco, Google, Mozilla and Oracle, all have recently credited AI-assisted research with increasing their patch cadence and volume (Google said today it is now going to ship security updates every two weeks).
Tyler Reguly, associate director of security research and development at Fortra, said one core challenge with deploying Windows updates is that they need to be tested before being installed across an organization because not all third-party software works seamlessly in the face of changes to the underlying operating system.
“It’s time to put our CISOs and CSOs on notice,” Reguly said. “How are you helping your teams through these difficult times? Do you have your teams deploy after hours and on weekends to avoid disruption to the business environment? Do you reward them for that effort? Time to dig into your budget and buy dinner for your teams that are working on Saturday to get patches rolled out before users return to work on Monday.”
Satnam Narang is senior staff research engineer at Tenable. Narang said it’s important to recognize that while the number of vulnerabilities being patched by Microsoft is rising, the number of flaws that can and will affect most organizations remains quite low.
“AI-assisted vulnerability discovery in 2026 is creating larger haystacks, but it isn’t finding more needles,” he said. “It’s critical that organizations understand which vulnerabilities actually apply to them, whether they pose a threat by being reachable and exploitable, and prioritize remediation based on this risk context.”
Of course, regular Windows users don’t need to test patches before deploying them, but they still need to open Windows Update periodically or else assent to the program’s nag notices about pending updates. And at the rate these Windows patch releases are ballooning in size, it’s probably best not to let them pile up month after month.
Enterprise Windows admins will want to keep an eye on askwoody.com for news of any updates that appear to be causing problems. As always, the SANS Internet Storm Center has a per-patch breakdown ordered by severity and urgency.
The source text above remains the property of its publisher and is reproduced for commentary.